NVIDIA Confidential Computing is adding Confidential Bare Metal, a deployment option designed to let frontier model builders run sensitive workloads on dedicated third-party infrastructure while retaining control of their models, data and software stack. The expansion gives developers another way to use outside computing capacity without adopting a virtualized environment.
Key Takeaways
- Confidential Bare Metal lets model builders operate their own software stack on dedicated third-party NVIDIA infrastructure.
- Cohere plans to integrate the option into Model Vault, while Google Cloud is extending support to A4X Max instances.
- Platform support is expanding across Grace Blackwell and Rubin systems; DSX OS support and systems-partner capabilities are planned.
Table of Contents
- What NVIDIA Confidential Computing changes
- How the deployment options differ
- What Cohere and Google Cloud are doing
- Where platform support stands
- Conclusion
What NVIDIA Confidential Computing changes
The central change is the combination of confidential computing protections with control over a bare-metal software environment. NVIDIA says model builders can own and operate a bespoke stack, including host and platform infrastructure software, across third-party cloud, neocloud and enterprise infrastructure.
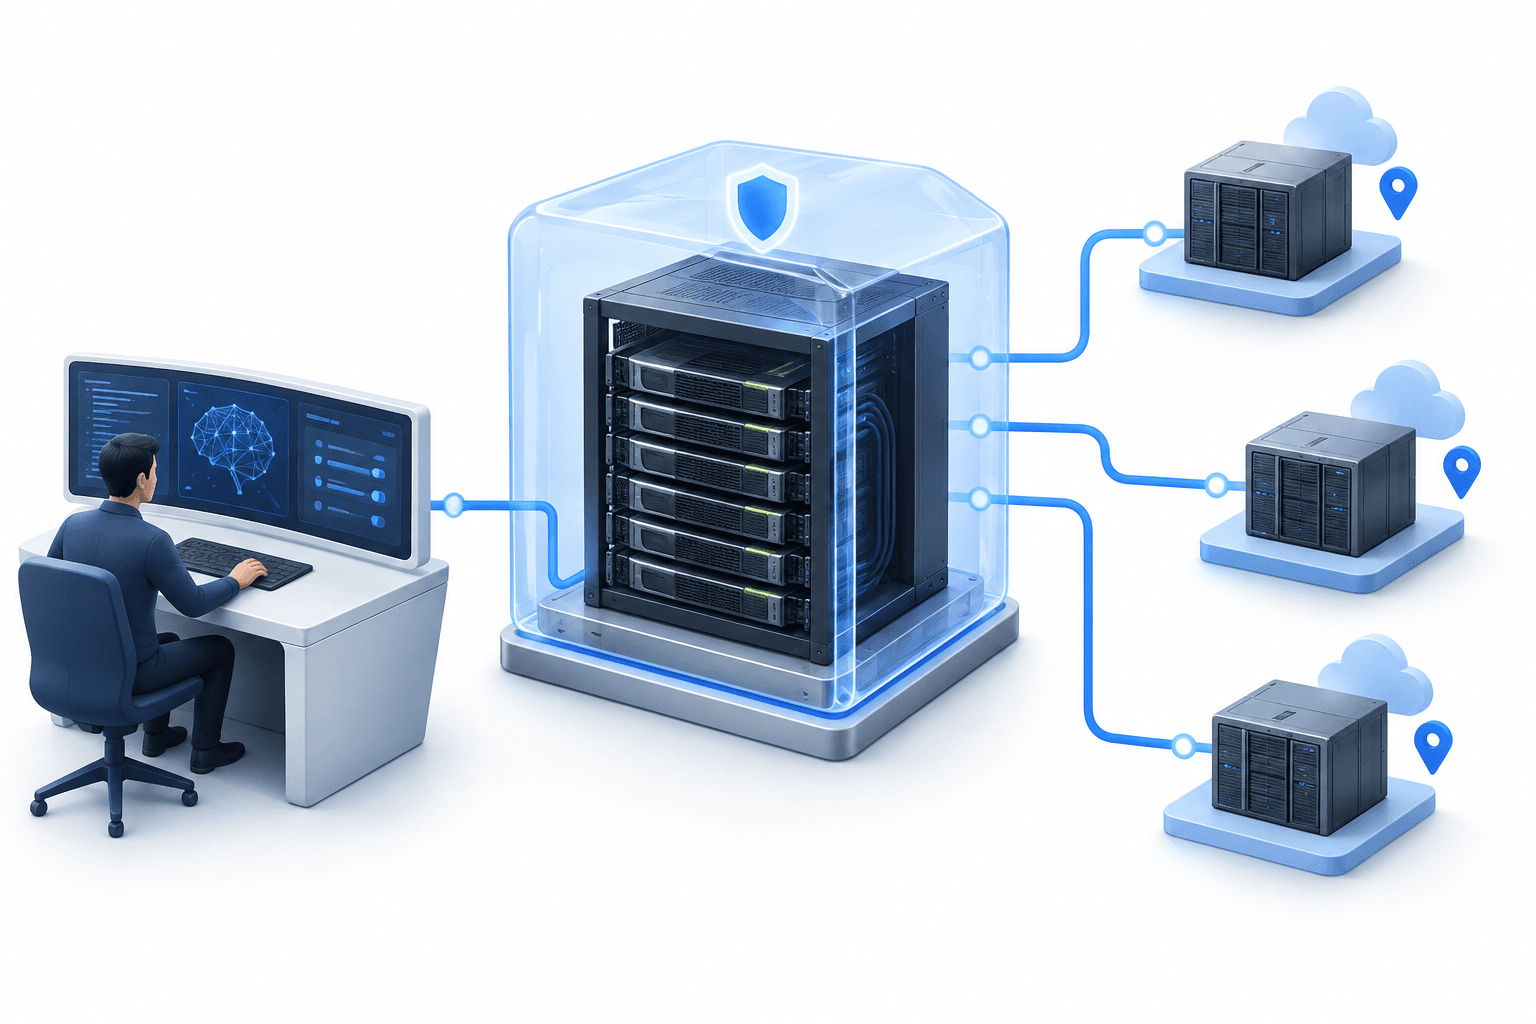
The company is introducing platform security controls intended to protect data in transit, measure platform integrity and enforce hardware-level access restrictions. Its confidential computing architecture uses hardware-rooted isolation and cryptographic attestation to help protect models and data during execution.
For builders seeking additional training and inference capacity, NVIDIA positions the expansion as a way to access more geographic, sovereign and operational options. Supported infrastructure providers, in turn, gain a path to serve sensitive workloads that require strong model and data privacy protections.
| Item | Details |
|---|---|
| Confidential Bare Metal | New deployment option for sensitive workloads on dedicated third-party infrastructure, with builder control over the software stack. |
| Confidential Containers | Deployment option for Kubernetes environments within NVIDIA’s converged security architecture. |
| Confidential Virtual Machines | Deployment option for virtualized environments. |
| Cohere Model Vault | Cohere plans to integrate Confidential Bare Metal using NVIDIA trusted execution environments. |
| Google Cloud | Extending Confidential Bare Metal support to A4X Max instances powered by NVIDIA GB300 NVL72 systems. |
| NVIDIA DSX OS | Will support all NVIDIA Confidential Computing modes for providers building AI factories. |
How the deployment options differ
Bare metal joins Confidential Containers and Confidential Virtual Machines in what NVIDIA describes as a converged security architecture. The distinction is the operating environment: dedicated bare-metal infrastructure, Kubernetes environments or virtualized environments.
That choice matters because organizations can select a deployment model that matches their trust boundaries and operating requirements. The new option specifically targets builders that want to run their own host and platform software rather than use the container or virtual-machine deployment models.
What Cohere and Google Cloud are doing
Cohere plans to integrate Confidential Bare Metal into Cohere Model Vault. The planned integration would use NVIDIA Confidential Computing trusted execution environments to extend hardware-rooted security to the GPU, protecting models and data in memory and across interconnects during execution.
Google Cloud is extending Confidential Bare Metal support to A4X Max instances powered by NVIDIA GB300 NVL72 systems. NVIDIA says those instances will combine non-virtualized accelerated computing with cryptographic protection for training data and model intellectual property.
These are distinct adoption steps: Cohere describes a planned integration into its model platform, while Google Cloud is extending infrastructure support. Neither should be treated as evidence that every provider in NVIDIA’s broader ecosystem has completed a Confidential Bare Metal rollout.
Where platform support stands
NVIDIA says Confidential Computing support now extends to Grace Blackwell NVL72 rack-scale systems, as well as x86-based HGX Rubin NVL8 and DGX Rubin NVL8 systems. This broadens the hardware platforms covered by the security architecture.
The company names CoreWeave, Firmus, GMI Cloud, Google Cloud, IREN, Lambda, Microsoft Azure Infrastructure, Nebius, Nscale and Vultr as supporting NVIDIA Confidential Computing deployments. That ecosystem statement covers Confidential Computing generally, rather than establishing identical deployment options at every provider.
Further support remains forward-looking. Cisco, Dell Technologies, HPE, Lenovo, Supermicro and Bull will support the capabilities through NVIDIA-Certified Systems. NVIDIA DSX OS will also support all Confidential Computing modes, providing a software foundation for cloud providers building and operating AI factories with confidential workloads.
Conclusion
The expansion gives model builders a confidential computing option built around dedicated infrastructure and software-stack control. Its practical reach combines newly extended hardware support with provider-specific steps, including Cohere’s planned integration and Google Cloud’s infrastructure expansion.
Read More News
Disclaimer
This FinanceVelix article provides general information, not personalized financial, investment, legal, or tax advice. Market prices, interest rates and economic conditions can change; investments carry a risk of loss. Facts reflect the material available when published and may change. Check important information independently and consult a qualified professional when needed. Mentioning an asset, company, or service is not an endorsement.