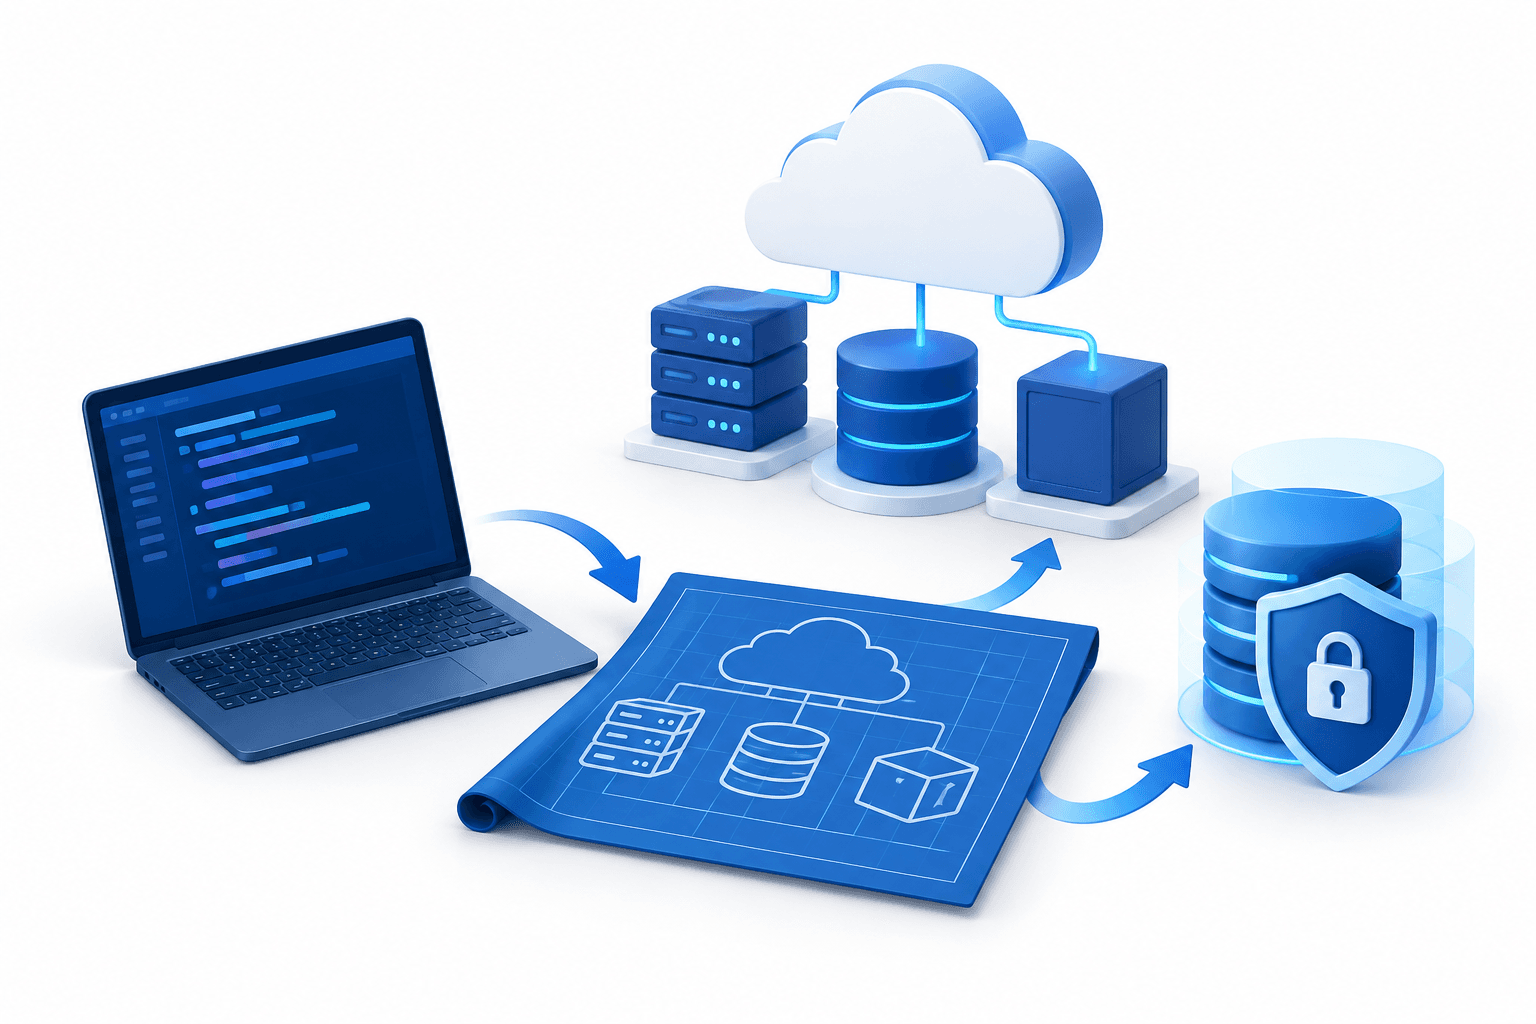
Cohesity cloud rebuild has become the first cloud recovery method validated for interoperability with IBM Terraform Self-Managed, Cohesity said on October 27, 2026. The feature combines Terraform infrastructure code with Cohesity backups to help organizations recover cloud applications after a cyberattack.
Key Takeaways
- Terraform recreates the declared infrastructure configuration, while Cohesity restores application data from backup.
- Administrators can see the timing gap between the selected code version and its paired data backup.
- Cloud rebuild is available in Cohesity Data Cloud Enterprise Edition.
How Cohesity cloud rebuild works
The feature uses an organization’s reviewed infrastructure-as-code files as a blueprint for recovery. Terraform recreates the declared configuration, including resources such as networks and servers, and Cohesity restores usable application data from backup.
Cohesity said the approach is intended to return an application to its declared configuration rather than reproduce a pre-attack environment that might already contain an attacker’s changes. The validation covers interoperability with Terraform Self-Managed, a self-hosted platform for managing infrastructure as code.
Recovery points and availability
Cloud rebuild maps the resources that need protection and their restoration order. It backs up Terraform code and application data over time, allowing teams to select a recovery point and see the data backup paired with it.
Infrastructure and data backups can run on different schedules, so the feature shows the time difference between them. For databases such as Amazon RDS, a guided process helps administrators reconnect a restored database to the application.
Cohesity said cloud rebuild is available as part of Data Cloud Enterprise Edition. Existing Data Protect or NetBackup customers can upgrade to that edition to access the feature.
Survey points to recovery planning gaps
In a Cohesity-commissioned 2026 survey by Vanson Bourne, 83% of 3,200 security and IT decision-makers said their organizations’ recovery plans needed moderate or significant changes to handle attacks using AI to find and exploit software weaknesses. Just 3% said their plans were ready.
Read More News
Disclaimer
This FinanceVelix article provides general information, not personalized financial, investment, legal, or tax advice. Market prices, interest rates and economic conditions can change; investments carry a risk of loss. Facts reflect the material available when published and may change. Check important information independently and consult a qualified professional when needed. Mentioning an asset, company, or service is not an endorsement.




Comments
Be respectful. No spam, impersonation or private credentials. Ordinary posts and comments appear immediately; suspicious links are held for review.
Please wait…